AnyPwn: unauth root on AnyDesk Linux 8.0.2
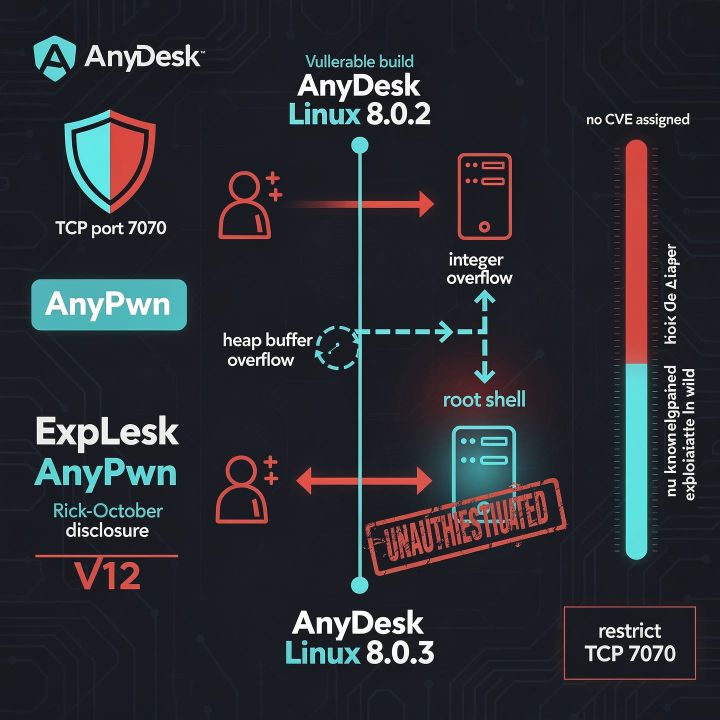
AnyDesk Linux 8.0.2 has a memory-corruption flaw letting unauthenticated attackers get root via TCP port 7070, bypassing login and session controls. AnyDesk 8.0.3 is the fix; no exploitation in the wild has been reported at disclosure.