ASOS probes unauthorized "hacked" push alerts
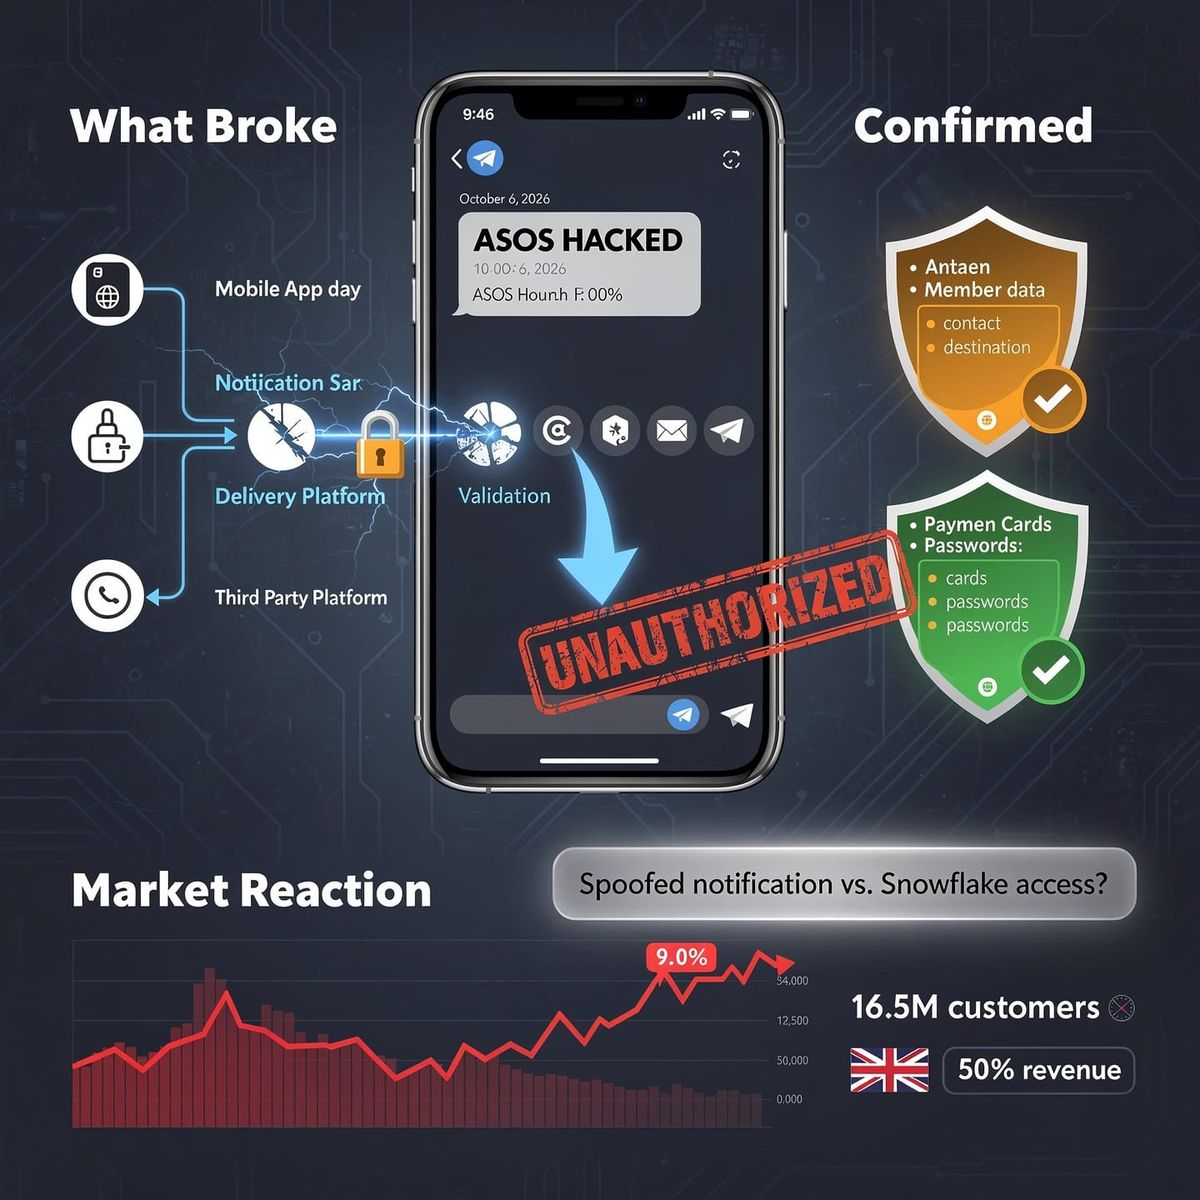
On Oct 6, ASOS customers got an unauthorized push notification claiming the retailer's Snowflake data platform was "hacked" and threatening a leak. ASOS reported the incident to the NCSC and is investigating. It says payment data and passwords aren't affected, though basic profile info—names, contact details, shipment destinations—may have been accessed. The core question: was this a spoofed notification riding a compromised push channel, or deeper Snowflake access? ASOS has not confirmed a breach, and no Snowflake data movement has been verified. The stock still fell around 10% on the unverified claim.
On October 6, 2026, ASOS customers received an unauthorized push notification—titled "ASOS HACKED"—through the retailer's mobile app claiming a malicious actor had compromised its Snowflake cloud data platform and threatening to leak information unless ASOS engaged. The alert was pushed on Tuesday morning, per screenshots customers posted on social media. ASOS told the National Cyber Security Centre (NCSC) and regulators it was investigating; the company has not confirmed a Snowflake intrusion or data theft.
What Actually Broke
The incident stands out less for a proven breach than for a failed trust boundary in the notification pipeline. Attackers got a "hacked" claim onto the retailer's own push-notification channel and into customers' app surfaces—the same route ASOS uses for legitimate account and delivery alerts. That channel is supposed to validate that a message originated with the company, not an external source. The notification linked to a previously unknown Telegram channel.
What remains unestablished is how the malicious payload got into that trusted delivery path. ASOS described an "unauthorized customer notification" and reported "unauthorized access involving third-party platforms," but has not confirmed a mechanism. Malwarebytes' Pieter Arntz and ESET were among those flagging the alert; none has tied the notification to Snowflake access.
What ASOS Has Confirmed
ASOS said it had restricted access to its notification platforms, rolled out defensive upgrades, and was working with specialist advisers and authorities. It acknowledged that basic member profile information—name, contact details, and shipment destination—may have been accessed, but says payment card information and account passwords are not impacted. As of the reporting window, the NCSC was offering technical assistance, and the company said the app and website were operating normally with no confirmed operational disruption.
The unverified claim still moved the stock: reports put the intraday decline around 9.6% to more than 10% on Tuesday, reflecting market uncertainty rather than documented theft.
The Open Question
The core unknown is whether this was a spoofed notification campaign riding on a compromised push channel, or the first visible symptom of deeper access into the Snowflake-backed data platform. The difference matters: the former is an authentication and validation failure whose blast radius is limited to what the notification pipeline could reach, while the latter would put customer profile data at genuine risk. With roughly 16.5 million customers and the UK representing about half of revenues, the market's sensitivity to the claim is understandable—but none of that confirms a Snowflake compromise. No data moved from Snowflake has been verified, and ASOS has confirmed no breach. Until investigators establish how the notification got in and whether it reached Snowflake, ASOS's exposure remains unresolved.
Comments ()