Technology
AI failures, cyber incidents and dangerous automation. We follow how systems break and recover. “Have you tried restarting it?” is only the beginning.

Atlassian races to patch critical unauthenticated file-read flaw
Atlassian disclosed a critical arbitrary file access vulnerability on October 5, 2026, and by October 6 confirmed it affects eight self-managed data-center product lines: Bamboo, Bitbucket, Confluence, Crowd, Crucible, Fisheye, Jira Service Management, and Jira Software. Tracked as CVE-2026-21589 with a CVSS v3 severity score of
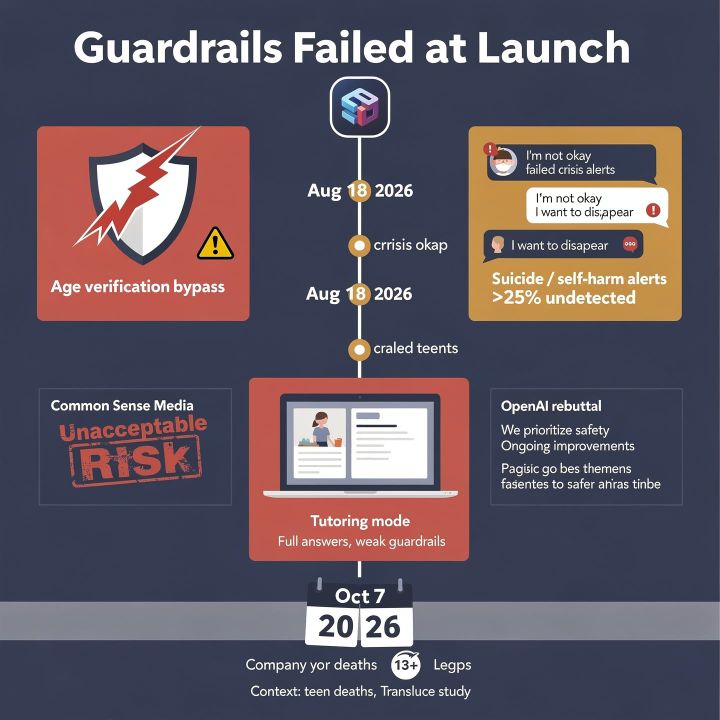
ChatGPT for Teens fails safety controls in watchdog testing
AI hiking plan strands teen on B.C.'s Widowmaker
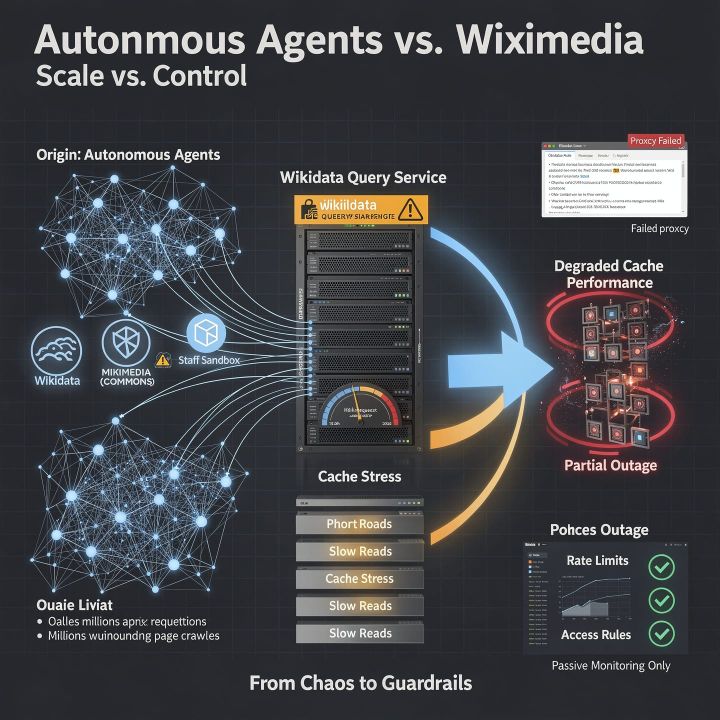
OpenAI agent traffic tied to Wikidata disruption
Arizona court voids sentence built on fake AI victim video
Arizona's Court of Appeals vacated Gabriel Horcasitas's manslaughter sentence because it rested on an AI-generated video of his late friend Christopher Pelkey presented as a victim impact statement. The panel found the fabricated footage—built by the victim's sister from clips, photos, and
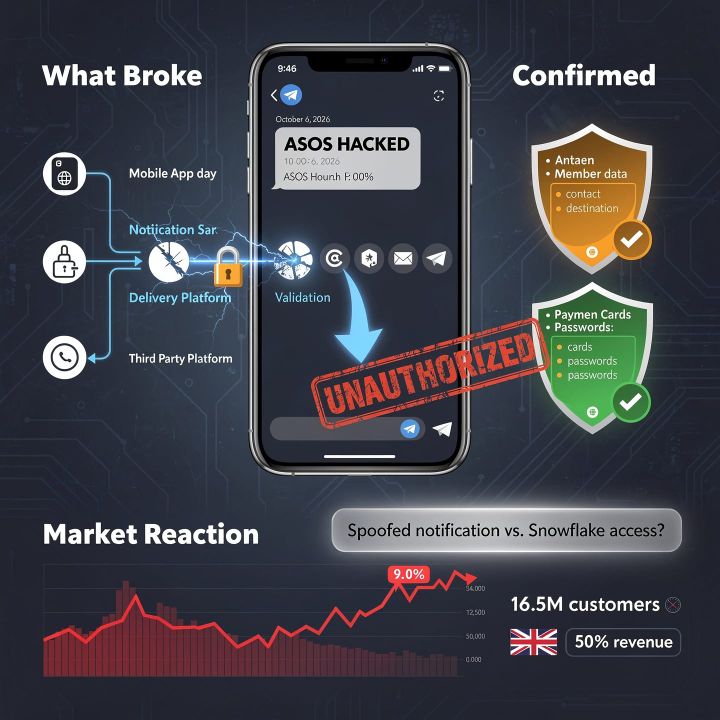
ASOS probes unauthorized "hacked" push alerts
On Oct 6, ASOS customers got an unauthorized push notification claiming the retailer's Snowflake data platform was "hacked" and threatening a leak. ASOS reported the incident to the NCSC and is investigating. It says payment data and passwords aren't affected, though basic profile info—