CISA: Two Exploited Cisco Flaws; Commissary Cause Unresolved
CISA's KEV catalog now lists two exploited Cisco flaws: an unauthenticated SD-WAN Manager privilege escalation rated 9.8, and an ISE authentication bypass with no workaround beyond upgrading. The August commissary refrigeration failures are still under investigation, with no root cause established.
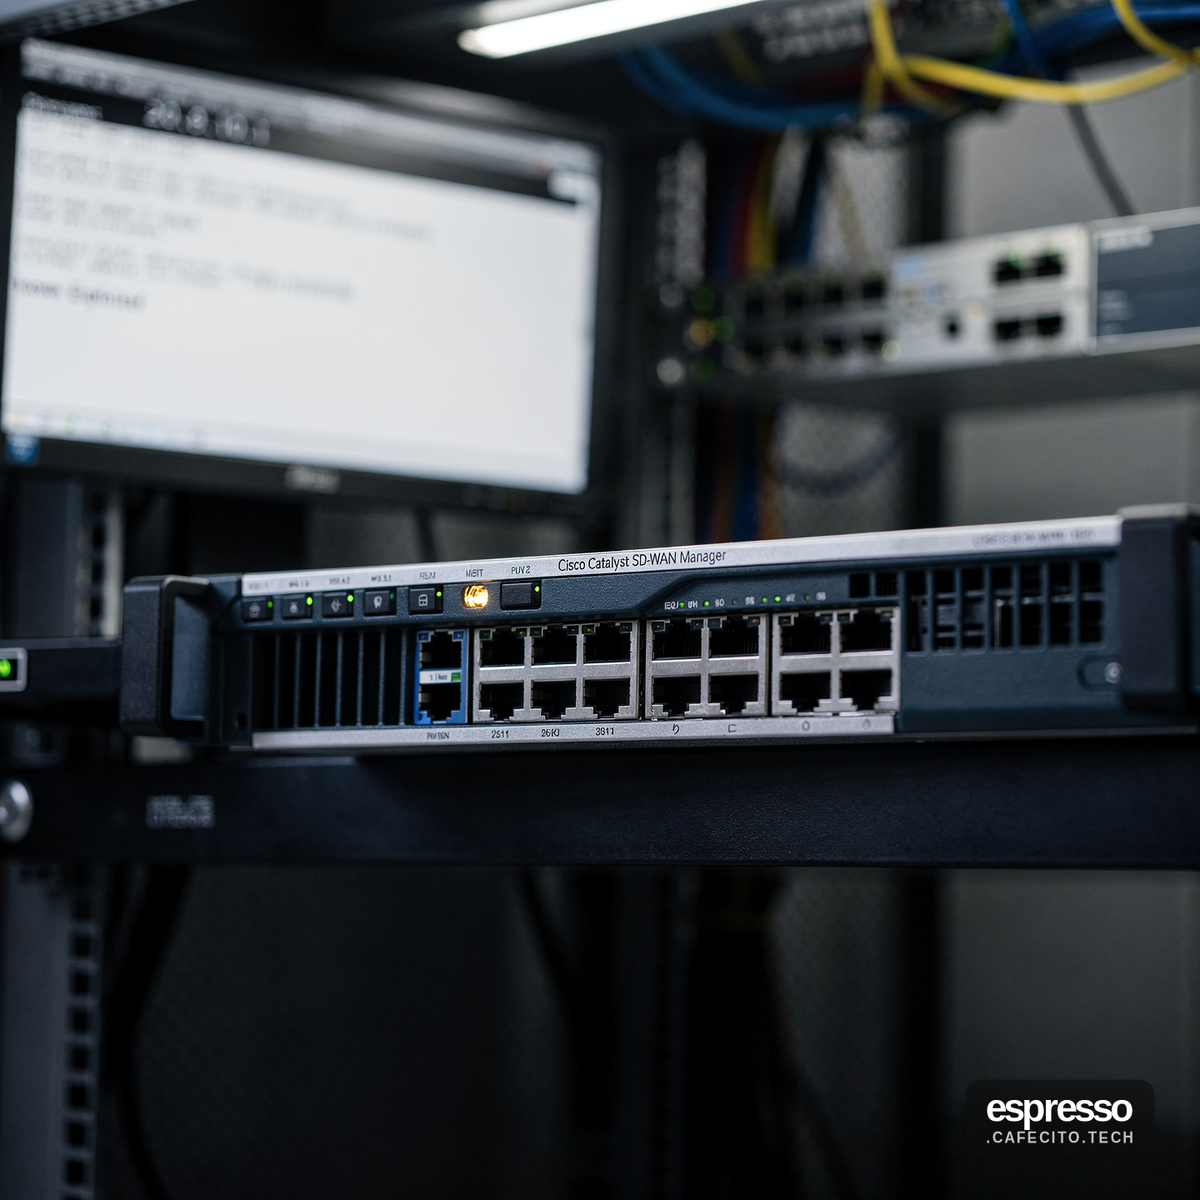
Two actively exploited Cisco vulnerabilities dominate this week's patching record. CISA added CVE-2026-76504, an unauthenticated remote privilege-escalation flaw in Cisco Catalyst SD-WAN Manager caused by improper URI encoding handling, to its Known Exploited Vulnerabilities catalog on September 30, 2026, per supplied events. CISA set a remediation deadline of October 3 under binding directive BOD 26-04, issued June 10, 2026. The CVSS v3.1 base score is 9.8 (CWE-177); Cisco tracks it as CSCww79570, and guidance points to patched releases including 20.9.10.1 and 20.12.8.2, disabling the manager on unsecured networks, and firewall filtering.
Separately, CVE-2026-76460 affects Cisco Identity Services Engine and ISE Passive Identity Connector. Supplied accounts describe an unauthenticated authentication bypass in an API endpoint, exploited in the wild and confirmed during Cisco TAC case work; CISA added it to the KEV catalog on September 16, 2026. Fixed builds run from ISE 3.1 Patch 12 through 3.5 Patch 4, with no workaround beyond upgrading. Reported potential impacts include root-level command execution and removal of forensic evidence. A second supplied account sets a federal patch-or-disable deadline of September 19 — after CISA's September 16 listing.
What the Mechanism Allows, and What It Does Not
Both flaws sit at the same boundary: management interfaces reachable without proving identity. In the ISE case, the stated prerequisite is network reach to a web-based management interface; the failed validation is authentication itself. For SD-WAN Manager, a crafted HTTP request's URI encoding bypasses controls, granting admin-level privileges unauthenticated. CVSS describes severity, not how many organizations were reached.
Commissaries: Exposure Measured, Attribution Open
Refrigeration failures disrupted military commissaries across nine states on August 26–30, 2026, one supplied event states, with at least 12 affected and chilled or frozen sales restricted, online ordering suspended, and inventory spoilage reported. A second account says at least six commissaries and cites Fort Huachuca, where freezers reportedly switched to defrost mode on August 26. Neither attribution nor root cause is established; a technical fault also remains under consideration. Supplied accounts differ on recovery: Newport resumed August 29 and NAS Lemoore August 28; another describes partial resumption from mid-August.
The DCIS-led joint investigation, working with Army CID's Cyber Field Office, Defense Cyber Defense Command, US Cyber Command, and French law enforcement per supplied events, treats the failures as suspected cyberattacks. Earlier research on internet-exposed refrigeration controllers — Claroty's Team82 in August, plus February and May 2025 CISA advisories on Copeland XWEB and Danfoss AK-SM 8xxA devices — establishes a vulnerable device class, not exploitation of commissary systems. Coalition counted 1,506 unique IPs exposing Danfoss StoreView admin panels between September 7 and October 6, 820 on French networks; 618 Danfoss devices remained internet-connected as of mid-October (206 French, 50 US, 2 UK). Reachability is not compromise.
French authorities are investigating a separate campaign: food spoilage and reported fires across chains, with one account describing 150–200 Intermarché stores and fewer than 100 Coopérative U outlets. A shared device class and targeting theme do not establish a common actor or link to the US outages.
The Tests That Would Resolve It
Three observable findings would move the commissary question from suspicion toward attribution: forensic artifacts from the named controller models at affected sites, network logs showing unauthorized commands reaching commissary monitoring systems, or French technical findings matching signatures on US devices. Absent any, documented internet exposure remains the measured fact and exploitation remains unresolved, with the investigation described as ongoing. No root cause has been identified.
Comments ()